The short answer
The Digital Personal Data Protection Act, 2023 applies to every Indian hotel that collects guest data digitally. The DPDP Rules were notified in November 2025, and most obligations phase in over 18 months, to around May 2027. Hotels need lawful purpose or consent, clear notices, defined retention, secure vendors, breach response and trained staff before then.
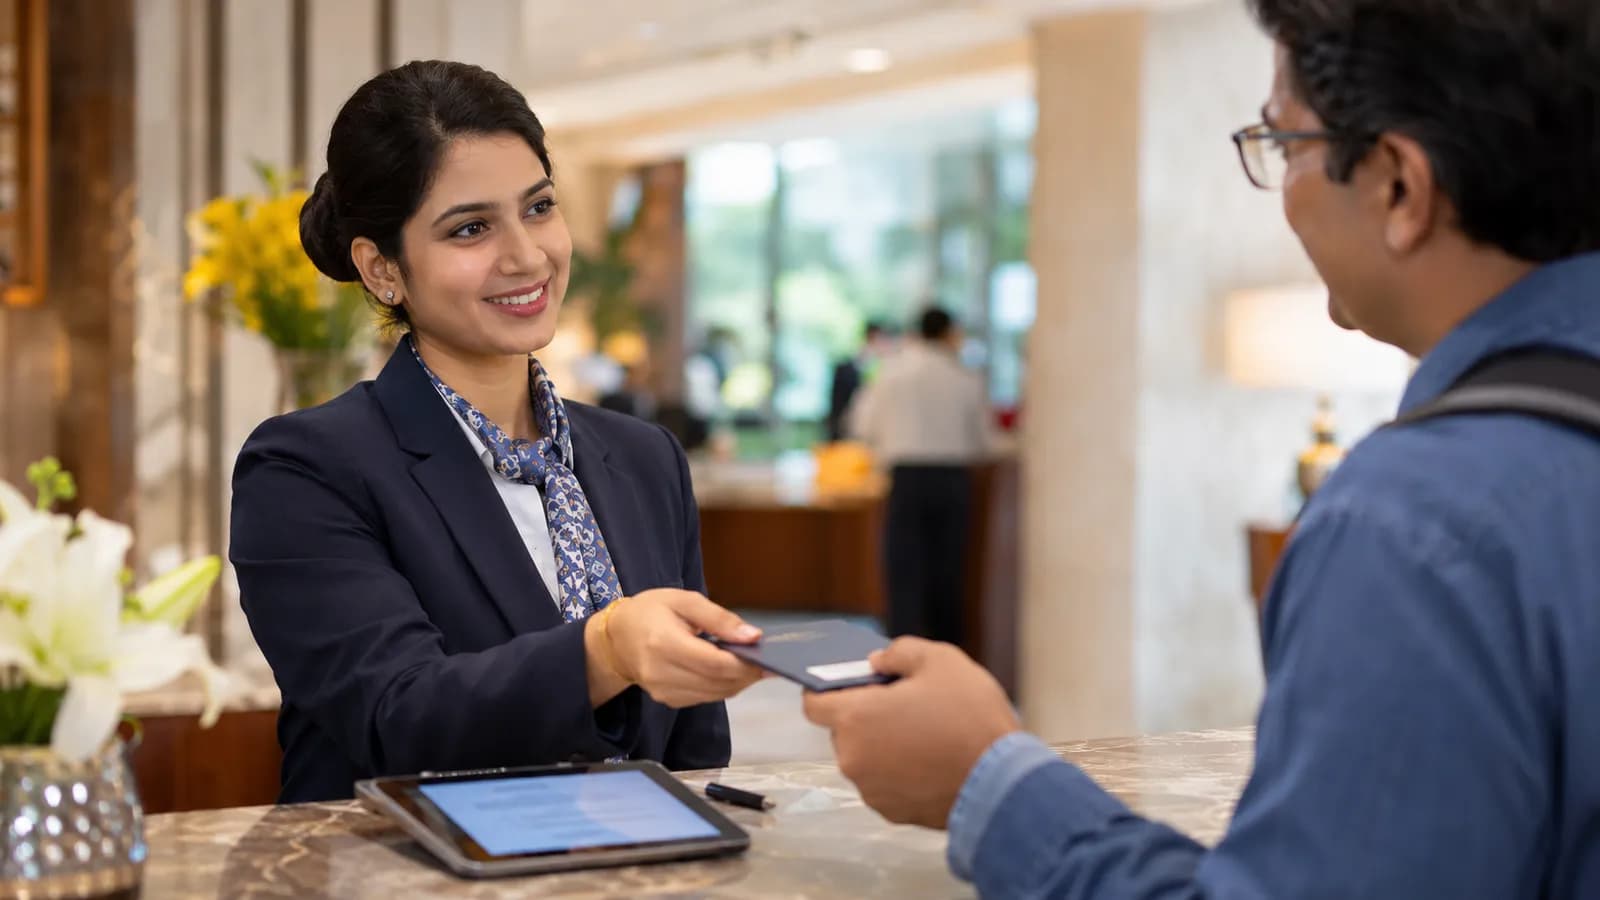
Few small businesses handle as much personal data as a hotel. In a single stay you may collect a guest's name, phone number and email, a copy of their Aadhaar or passport, their payment details, their arrival and departure times, their dietary preferences, their car number at the gate and hours of their movement on CCTV. Most of it now sits in digital systems — the PMS, the booking engine, the channel manager, a WhatsApp group at the front desk, and more than a few spreadsheets.
India's Digital Personal Data Protection Act, 2023 turns how you handle that data into a legal obligation, not just good manners. The DPDP Rules were notified in November 2025, and most obligations phase in over roughly 18 months, which most commentators place in May 2027. That sounds like a long runway. For a hotel that has never mapped its data, it is not. This is a practical overview for owners and GMs, not legal advice — confirm specifics with counsel and the official notification.
Does the DPDP Act apply to my hotel?
Almost certainly. The Act applies to digital personal data of individuals in India, and there is no blanket exemption for small or independent businesses. In the Act's language, your hotel is a Data Fiduciary — the party that decides why and how guest data is processed. Your PMS provider, booking engine, OTA partners and marketing agency are typically Data Processors acting for you, and you remain answerable for what they do with data you share.
What data does a hotel actually hold?
The first job is to find out. Most hotels underestimate how many places data lives.
| Data | Where it usually sits | Why it is collected |
|---|---|---|
| Guest identity and ID copies | PMS, scanner folder, paper register | Legal reporting, security |
| Foreign national details | PMS, Form C portal | Mandatory FRRO reporting |
| Contact details | PMS, booking engine, WhatsApp | Booking and communication |
| Payment data | Gateway, POS, card machine | Settlement |
| Preferences and history | PMS guest profile, CRM | Service, repeat business |
| CCTV footage | DVR/NVR | Safety and security |
| Staff records | HR files, payroll | Employment |
| Marketing lists | Email and WhatsApp tools | Promotion |
What does the law actually ask hotels to do?
In practical terms, the obligations reduce to a handful of disciplines. Process data only for a lawful purpose, either with the guest's consent or under a recognised legitimate use such as complying with a legal requirement. Give a clear notice explaining what you collect and why. Collect only what the purpose needs. Keep it accurate. Protect it with reasonable security safeguards. Delete it when the purpose is served and no law requires you to keep it. Notify the Data Protection Board and affected individuals if there is a breach. And give guests a way to ask about, correct or withdraw consent for their data.
How should hotels handle ID copies?
This is the most sensitive area for Indian hotels. Many properties photocopy or photograph every guest's ID and keep it forever, in a folder on a shared computer or a front-desk phone. Collecting ID where a legal requirement exists is not the issue; Form C reporting for foreign nationals and local police requirements remain. The issues are excess and retention. Collect what the requirement needs, mask what it does not, keep scans in a controlled system rather than personal devices, restrict access to named roles, and set a deletion schedule tied to the legal retention period.
What about vendors and OTAs?
Your hotel is only as compliant as the systems it shares data with. Review contracts with your PMS, booking engine, channel manager, payment gateway, CCTV maintainer and any marketing or WhatsApp platform. You want clarity on where data is stored, who can access it, how breaches are reported to you, and how data is returned or deleted when the contract ends. The hotel technology stack you already run is the right place to start that inventory.
What happens if there is a breach?
A breach is not only a hack. A lost front-desk phone with guest ID photos, a misdirected email with a rooming list, or a former employee with live PMS access are all breaches. Have a written response plan before you need it: who is told internally, how the breach is contained, who assesses its scope, and how notification to the Board and affected guests happens. The Act allows for penalties of up to ₹250 crore for some failures, and while actual penalties will depend on circumstances, the reputational cost of a guest-data leak is immediate.
Who owns this inside the hotel?
Someone has to. In a single property this is often the GM, supported by the front-office manager and whoever manages IT. In a group, it may be a designated compliance lead. The point is that data protection becomes part of your operating system, with SOPs, training at induction and an annual review — not a policy document written once and filed.
Does CCTV footage count as personal data?
Yes. Footage that shows identifiable guests and staff is personal data, and the same principles apply: a clear purpose (safety and security), notice through visible signage, access restricted to named people, and a defined retention period after which recordings are overwritten. Requests from police or other authorities should be logged and handled through one person, not answered informally by whoever is on duty.
Where to start this month
- Map your data — every system, folder, device and paper register that holds guest or staff data.
- Rewrite your guest notice at booking and check-in in plain language.
- Separate marketing consent from booking communication and record it.
- Fix ID handling — controlled storage, restricted access, a deletion schedule.
- Review vendor contracts for storage, access, breach notification and deletion.
- Write a breach response plan and name the people in it.
- Train every front-office and reservations employee before the deadline, not after.
May 2027 will arrive faster than most hotels expect, and the properties that start now will find the work far less disruptive. If you want help building data-protection SOPs into your front office and reservations, book a strategy call.
Owner's guides
Brand selection, pre-opening & feasibility playbooks — download instantly.
Frequently Asked Questions
Quick answers on the dpdp act and hotels: what guest-data compliance means before may 2027.
Yes. The Act applies to any organisation that processes digital personal data of individuals in India, and there is no general exemption for small hotels. If your hotel stores guest names, phone numbers, ID scans or booking details in a PMS, spreadsheet, booking engine or WhatsApp, it is processing personal data under the Act.
The DPDP Rules were notified in November 2025, with most substantive obligations phased in over about 18 months, which most commentators place in May 2027. Some provisions took effect earlier. Check the official gazette notification or your legal adviser for the exact dates that apply to each obligation.
Hotels can collect identity documents where the law requires it, such as police or local reporting requirements and Form C reporting for foreign nationals. What changes is discipline: collect only what the requirement needs, tell the guest why, store it securely, restrict who can see it, and delete it when the retention requirement ends rather than keeping it indefinitely.
The Act sets penalties that can reach up to 250 crore rupees for certain failures, such as not taking reasonable security safeguards to prevent a personal data breach. Actual penalties are decided by the Data Protection Board based on the nature and severity of the breach.
For marketing, plan on clear, specific consent that the guest can withdraw as easily as they gave it, and keep a record of it. Operational messages tied to a booking rest on a different footing from promotional ones. Separate the two lists, record when and how marketing consent was given, and honour opt-outs promptly.
Written by
Rachit Goel
Founder & Principal Hospitality Consultant
Founder of The Hotel Adviser and a hospitality leader with 25+ years of hands-on experience across Marriott, Radisson, Ramada and Taj — spanning pre-opening, operations, revenue management and food & beverage.